How Essential Eight Builds Cyber Resilience Through Discipline, Not Tools
 Niten Devalia
Chief Sales Officer / Co-founder • Jan 14, 2026 • 5 min read
Cybersecurity conversations often focus on tools — new platforms, dashboards, and alerts. Yet many breaches still occur in environments filled with modern security technology. The issue is rarely a lack of tools; it’s a lack of foundational cyber discipline.
The Australian Cyber Security Centre’s Essential Eight exists to address this exact problem. It defines eight practical, proven strategies (not in any particular order) that significantly reduce the risk of cyber compromise when implemented and maintained correctly.
At Exigo Tech, we help organisations move beyond checkbox compliance and use Essential Eight as a framework for building measurable, sustainable cyber resilience.
Why Essential Eight Matters More Than Ever
Cyber threats have become:
- More targeted
- More automated
- Faster to execute
- Harder to detect early
Ransomware, credential abuse, and supply chain attacks routinely exploit basic security weaknesses rather than sophisticated zero-day vulnerabilities.
Essential Eight focuses on blocking the most common attack paths used by adversaries. When applied consistently, it dramatically reduces the likelihood and impact of successful cyberattacks.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
Essential Eight Is a Maturity Model, Not a Checklist
One of the most misunderstood aspects of Essential 8 is how it should be implemented.
It is not:
- A one-time project
- A tool purchase
- A static compliance document
Essential Eight is a maturity-based framework, with four maturity levels (0–3). Each level represents increasing consistency, coverage, and resilience.
True alignment requires:
- Ongoing assessment
- Operational ownership
- Continuous improvement
Understanding the Eight Strategies (Without the Jargon)
Each Essential 8 control targets a specific risk area:
- Application Control
Stops unauthorised or malicious software from running.
- Patch Applications
Reduces exposure to known vulnerabilities in commonly exploited software.
- Configure Microsoft Office Macros
Prevents malicious macro-based attacks.
- User Application Hardening
Limits risky behaviours such as untrusted scripts and web content.
- Restrict Administrative Privileges
Minimises the damage attackers can do if access is gained.
- Patch Operating Systems
Closes system-level vulnerabilities before they are exploited.
- Multi-factor Authentication
Protects against credential theft and account compromise.
- Regular Backups
Ensures recovery is possible even after a successful attack.
Individually, these controls reduce risk. Together, they create layered protection that significantly raises the cost and complexity of an attack.
Benefits of Implementing the Essential Eight Properly
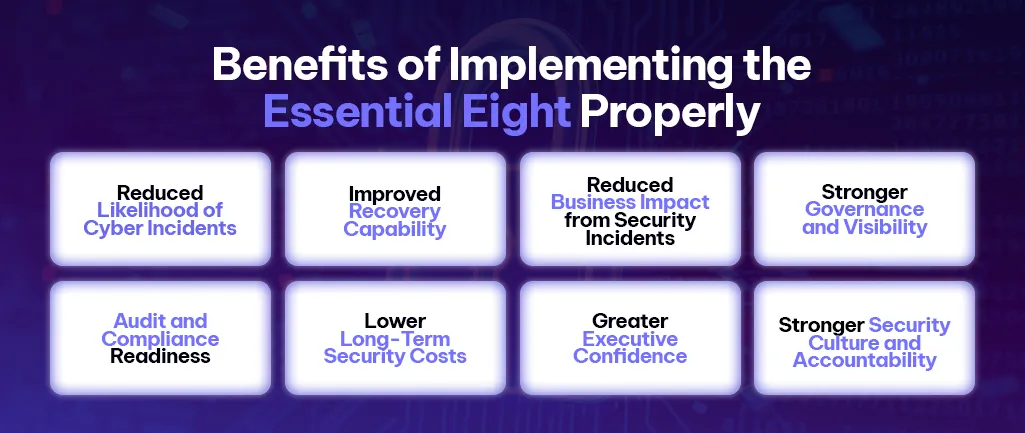
When Essential Eight is implemented as an ongoing security program, it delivers measurable benefits across risk reduction, governance, and operational resilience.
Reduced Likelihood of Cyber Incidents
Essential Eight directly blocks the most common attack techniques used in ransomware, malware, and credential-based attacks. Controls such as application control, patching, and privilege restriction prevent threats from executing in the first place, significantly lowering the probability of a successful breach.
Improved Recovery Capability
Regular, tested backups combined with access control and system hardening ensure that organisations can recover quickly and confidently after an incident. Recovery becomes a controlled process rather than a crisis, reducing dependence on emergency response measures.
Reduced Business Impact from Security Incidents
Even when incidents occur, Essential Eight limits their spread and severity. Restricted privileges, MFA, and hardened environments reduce lateral movement and data exposure, helping maintain business continuity and minimise downtime.
Stronger Governance and Visibility
Essential Eight provides a structured framework for understanding and managing cyber risk. Maturity levels, control ownership, and documented processes give leadership clear visibility into security posture and progress, supporting informed decision-making.
Audit and Compliance Readiness
Many regulatory bodies, cyber insurers, and auditors now expect alignment with Essential Eight principles. Proper implementation creates repeatable, evidence-based controls that simplify audits and demonstrate due diligence.
Lower Long-Term Security Costs
Preventing incidents is significantly more cost-effective than responding to them. By reducing breaches, downtime, and recovery efforts, Essential Eight lowers long-term spending on remediation, legal exposure, and unplanned security interventions.
Greater Executive Confidence
Clear maturity benchmarks and consistent reporting enable executives to understand cyber risk in practical terms. Leadership gains confidence that security investments are targeted, effective, and aligned with organisational risk tolerance.
Stronger Security Culture and Accountability
Essential Eight establishes clear responsibility for security controls, from patching to access management. This accountability fosters better security habits across IT teams and users, embedding security into everyday operations rather than treating it as an afterthought.

Agentic AI for Operations Leaders: Turning AI into Action
Common Mistakes Organisations Make with Essential Eight
Despite good intentions, many Essential Eight initiatives fall short due to:
- Treating maturity level achievement as the end goal.
- Implementing controls inconsistently across environments.
- Lack of ongoing monitoring and enforcement.
- Over-reliance on tools without process ownership.
- Poor documentation and evidence collection.
These gaps are often known during audits or even worse, after an incident.
How Exigo Tech Approaches Essential Eight
At Exigo Tech, Essential Eight is implemented as a managed security program, not a standalone project.
Our approach includes:
- Baseline maturity assessment.
- Risk-based prioritisation.
- Practical implementation aligned to business operations.
- Continuous monitoring and improvement.
- Clear reporting for leadership and auditors.
As a Managed Service Provider, we ensure controls remain effective long after initial implementation.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Essential Eight as a Foundation for Cyber Resilience
Essential Eight is not the ceiling of cybersecurity maturity; it is the foundation.
When embedded correctly, it enables organisations to:
- Adopt advanced security controls with confidence.
- Reduce noise from reactive security tools.
- Focus on resilience rather than recovery.
Cyber resilience is built through consistency, discipline, and accountability, not one-off initiatives.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

