Essential Eight Explained: Why Patch Operating Systems Should Be a Priority for Every Organisation
 Niten Devalia
Chief Sales Officer / Co-founder • Jan 26, 2026 • 4 min read
Operating systems sit at the very core of every IT environment. They control how devices run, how users access systems, and how applications interact with data. When operating systems are not patched, attackers don’t just gain access; they often gain control.
That’s why Patch Operating Systems is one of the most critical controls in the Essential Eight. While application patching reduces common entry points, operating system patching protects the foundation itself.
At Exigo Tech, we see operating system patching as one of the most effective ways to reduce high-impact cyber risk.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
What Does “Patch Operating Systems” Mean?
Patch Operating Systems means keeping operating systems updated with the latest security fixes and updates released by vendors. This includes:
- Windows and Windows Server
- macOS
- Linux distributions
- Mobile operating systems where applicable
These patches fix vulnerabilities that attackers can exploit to:
- Escalate privileges.
- Bypass security controls.
- Move laterally across systems.
- Disable security tools.
Operating system vulnerabilities are particularly dangerous because they operate below the application layer, giving attackers deep access to systems.
Why OS Vulnerabilities Are So Attractive to Attackers
When attackers exploit an operating system vulnerability, they often gain:
- Administrator-level access.
- Control over system processes.
- The ability to hide malicious activity.
- Access to other devices on the network.
Many major ransomware incidents have relied on known OS vulnerabilities that had already been patched by vendors, but not applied by organisations.
In simple terms, unpatched operating systems give attackers a powerful shortcut.
Why Operating System Patching Often Breaks Down
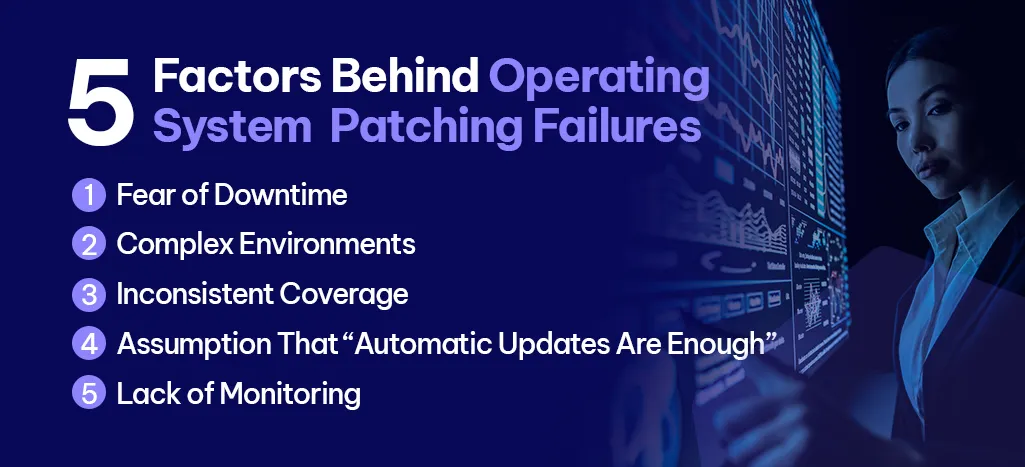
Despite its importance, OS patching is one of the most inconsistent security practices across organisations.
Common challenges include:
Fear of Downtime
Updates may require restarts or brief outages, so patches are delayed to avoid disruption.
Complex Environments
Multiple versions of operating systems across desktops, servers, and remote devices make coordination difficult.
Inconsistent Coverage
Some systems are patched regularly, while others are forgotten, especially remote or rarely used devices.
Assumption That “Automatic Updates Are Enough”
Automatic updates don’t always apply successfully and don’t cover all systems.
Lack of Monitoring
Many teams don’t verify whether patches were actually installed.
These gaps create opportunities that attackers actively look for.
Why Patch Operating Systems Is Essential Eight–Critical
The Essential Eight prioritises controls that stop attackers from gaining full control of systems. OS patching directly supports this goal by closing known vulnerabilities that enable privilege escalation and lateral movement.
Without effective OS patching:
- Other security controls are weakened.
- Recovery becomes more difficult.
- Attackers can move quickly once inside.
Essential Eight maturity expects operating system patches to be applied promptly and consistently, especially for high-risk vulnerabilities.

Agentic AI for Operations Leaders: Turning AI into Action
Benefits of Patching Operating Systems Properly
When OS patching is done well, organisations see significant security and operational benefits:
Reduced Likelihood of Major Cyber Incidents
Many high-impact attacks rely on OS vulnerabilities. Patching removes those attack paths.
Reduced Business Impact from Security Incidents
Even if an attacker gains initial access, patched systems limit escalation and spread.
Improved System Reliability
OS updates often include stability and performance improvements.
Stronger Security Tool Effectiveness
Security tools rely on a secure OS foundation to function properly.
Simpler Incident Response
Fewer vulnerabilities mean fewer critical incidents to investigate and resolve.
Improved Compliance and Audit Outcomes
Consistent OS patching supports Essential Eight maturity and regulatory expectations.
Common Mistakes Organisations Make with OS Patching
Even mature environments make avoidable mistakes:
- Delaying patches for long periods without risk assessment.
- Treating servers as “too sensitive to patch”.
- Ignoring non-critical or offline devices.
- Not testing patches in controlled phases.
- Assuming patch deployment equals patch success.
These mistakes often remain hidden until an incident occurs.
What Good Operating System Patching Looks Like
Effective OS patching is not about speed; it’s about discipline.
Good practices include:
- Clear patching schedules aligned to risk.
- Testing updates before broad deployment.
- Monitoring patch success and failures.
- Prioritising critical vulnerabilities.
- Maintaining visibility across all devices.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Why Choose Exigo Tech to Manage OS Patching
As a Managed Service Provider, Exigo Tech treats OS patching as a core security responsibility, not a background task.
We provide:
- Full visibility across endpoints and servers.
- Risk-based patch prioritisation.
- Controlled rollout to minimise disruption.
- Continuous monitoring and reporting.
- Alignment with Essential Eight maturity requirements.
Our goal is simple: keep systems secure without impacting operations.
Conclusion: OS Patching Is About Control, Not Convenience
Operating system patching is rarely exciting, but it is essential. It protects the core of your environment and reduces the risk of catastrophic security incidents.
When organisations treat OS patching seriously, attackers lose one of their most powerful advantages.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

