The Role of ‘Patch Applications’ in Essential Eight Controls to Reduce Cybersecurity Vulnerabilities
 Niten Devalia
Chief Sales Officer / Co-founder • Jan 21, 2026 • 5 min read
When organisations think about cybersecurity, they often focus on advanced tools like firewalls, endpoint protection, and monitoring platforms. Yet many successful cyberattacks don’t rely on sophisticated techniques. They exploit something far more basic: outdated applications.
Unpatched applications remain one of the most common entry points for ransomware and malware. That’s why Patch Applications is a core control in the Essential Eight. It is not a technical nice-to-have; it is a fundamental security requirement.
At Exigo Tech, we see application patching as a critical part of cyber risk management, not just a background IT task.
What Does “Patch Applications” Actually Mean?
Patch Applications means keeping all software up to date with the latest security fixes provided by vendors. This includes:
- Web browsers.
- PDF readers.
- Email clients.
- Java, .NET, and runtime environments.
- Line-of-business applications.
- Third-party tools installed across endpoints and servers.
It is important to understand that this is not the same as patching operating systems. Many organisations patch Windows or macOS regularly but leave applications outdated for months or even years.
Attackers know this. That’s why application vulnerabilities are one of their favourite targets.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
Why Unpatched Applications Are Such a Big Risk
Most cyberattacks don’t start with hacking passwords or breaking encryption. They start with a user opening a file, clicking a link, or visiting a website.
If an application is vulnerable:
- Malicious code can run without warning.
- Ransomware can be installed silently.
- Attackers can enter the environment easily.
Vendors regularly release patches to fix these weaknesses. When patches are not applied, organisations are effectively leaving known doors unlocked.
In many cases, the vulnerability used in an attack was:
- Publicly documented.
- Already patched by the vendor.
- Exploited simply because updates were delayed.
Why Application Patching Fails in Organisations
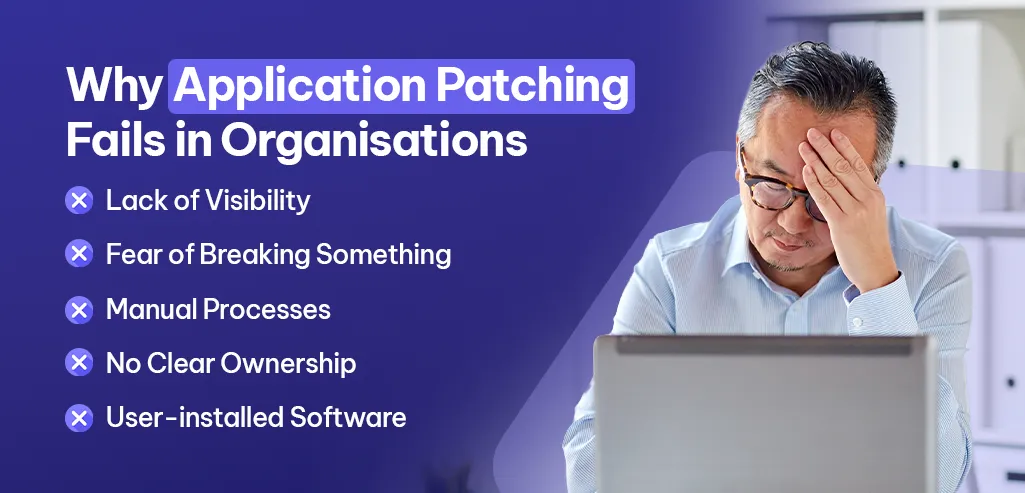
Application patching sounds simple, but in practice, it often breaks down.
Common reasons include:
Lack of Visibility
Many organisations don’t have a clear inventory of what applications are installed. If you don’t know what’s there, you can’t patch it.
Fear of Breaking Something
Teams worry that updates will cause compatibility issues or disrupt users, so patches are postponed indefinitely.
Manual Processes
Relying on manual updates leads to inconsistency, missed systems, and human error.
No Clear Ownership
Application patching often sits between security and IT operations, with no one clearly accountable.
User-installed Software
Employees install tools outside standard builds, creating unmanaged risk.
Why Patch Applications Is Critical to Essential Eight
The Essential Eight focuses on stopping common attack paths, not theoretical threats. Patch Applications directly addresses vulnerabilities that are actively exploited in the wild.
When combined with other controls such as application control and restricted privileges, patching becomes even more effective. Together, they make it significantly harder for attackers to succeed.
Essential Eight does not expect perfection overnight. It expects:
- Consistency
- Prioritisation
- Continuous improvement

Agentic AI for Operations Leaders: Turning AI into Action
Benefits of Patching Applications Properly
When application patching is done well, organisations see real, measurable benefits:
Reduced Likelihood of Cyber Incidents
Most attacks rely on known vulnerabilities. Patching removes those opportunities before attackers can use them.
Improved System Stability
Modern patches don’t just fix security issues; they often improve performance and reliability.
Lower Risk of Ransomware
Many ransomware infections begin through vulnerable applications. Patching closes that door early.
Simpler Incident Response
Fewer vulnerabilities mean fewer alerts, fewer investigations, and fewer emergencies.
Stronger Compliance Posture
Regular patching supports Essential Eight maturity, audits, and cyber insurance requirements.
Greater Confidence Across the Business
Leadership knows basic security hygiene is being maintained consistently.
Common Mistakes Organisations Make with Application Patching
Even well-intentioned patching efforts can fail due to common mistakes:
- Treating patching as an occasional task instead of a routine.
- Applying patches inconsistently across users and devices.
- Ignoring third-party applications.
- Not testing patches in controlled phases.
- Lacking documentation or reporting.
These gaps often only become visible after an incident or audit.
What Good Application Patching Looks Like
Effective application patching is:
- Proactive, not reactive.
- Automated, where possible.
- Prioritised, based on risk.
- Documented, for audit and reporting.
- Monitored, to ensure updates are successful.
It’s not about patching everything instantly; it’s about applying the right patches in the right way, consistently.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Why Choose Exigo Tech to Manage Application Patching
As a Managed Service Provider, Exigo Tech takes ownership of application patching as part of a broader security and operational framework.
Our approach includes:
- Full visibility of installed applications.
- Risk-based patch prioritisation.
- Controlled deployment to avoid disruption.
- Continuous monitoring and reporting.
- Alignment with Essential Eight maturity goals.
We don’t just apply patches; we manage the process, reduce risk, and keep systems stable.
Conclusion: Patching Applications Is About Discipline, Not Complexity
Application patching doesn’t require advanced tools or complex processes. It requires consistency, ownership, and follow-through.
When done properly, it removes one of the easiest attack paths available to cyber criminals and strengthens the foundation of your entire security posture.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

