Site Security Optimisation Services: Strengthen Security Across Your Business Locations
 Niten Devalia
Chief Sales Officer / Co-founder • Aug 26, 2026 • 5 min read
Businesses with multiple offices, branches, warehouses, facilities, and operational sites face a security challenge that is easy to underestimate.
Every location can have its own network, devices, users, applications, connectivity, and security configurations. Over time, these environments can become inconsistent, leaving gaps that attackers can exploit.
A new branch may be added without the same security controls as the head office. A firewall configuration may remain unchanged for years. Devices may connect to networks without adequate controls. Remote access may be enabled without regular review.
Site security optimisation addresses these gaps by assessing how each business location is connected, protected, monitored, and managed.
At Exigo Tech, we help organisations optimise site-level IT security as their Managed Intelligence Partner, creating consistent, secure, and manageable environments across distributed locations.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
What Is Site Security Optimisation?
Site security optimisation is the process of reviewing and improving the security controls operating at individual business locations and across the wider organisation.
Depending on the environment, this may involve reviewing:
- Network architecture
- Firewalls
- Wi-Fi security
- User access
- Endpoint protection
- Remote connectivity
- Cloud connectivity
- Monitoring and logging
- Device configuration
- Backup and recovery
The goal is not simply to add more security products.
It is to identify weaknesses, remove unnecessary exposure, and create a security architecture that is appropriate for the organisation’s operational requirements.
Why Multi-Site Businesses Face Greater Risk
A business with one location can often maintain a relatively consistent technology environment.
As the number of locations increases, complexity grows.
Different sites may have:
- Different internet providers
- Different network equipment
- Different firewall configurations
- Legacy devices
- Local administrators
- Different Wi-Fi arrangements
- Varying levels of security awareness
This inconsistency creates visibility and governance challenges.
A single weak location can potentially become an entry point into the wider corporate environment.
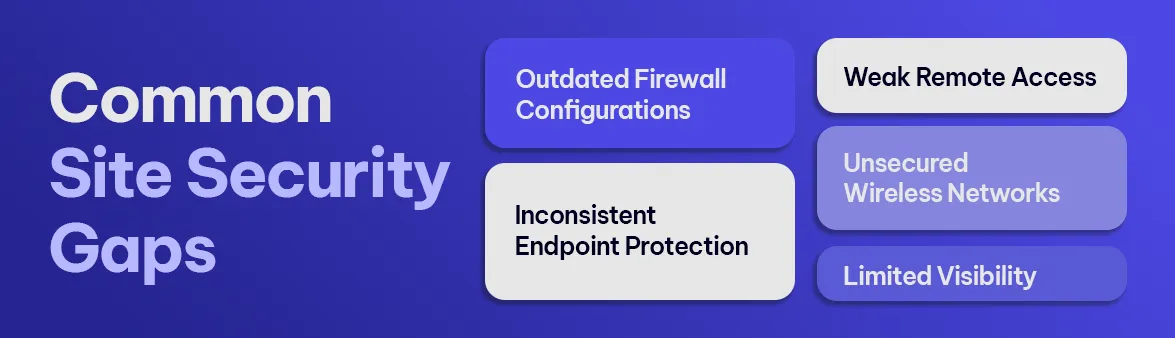
Common Site Security Gaps
-
Outdated Firewall Configurations
Firewalls provide an important layer of network protection, but their effectiveness depends on configuration.
Old rules, unnecessary ports, weak policies, and unused services can increase the attack surface.
Regular firewall reviews help ensure controls continue to match business requirements.
-
Unsecured Wireless Networks
Business Wi-Fi needs to be separated appropriately from guest and unmanaged devices.
Poorly configured wireless networks can expose internal resources to unnecessary risk.
-
Weak Remote Access
Remote access enables employees and service providers to work efficiently, but poorly controlled remote connectivity can create significant security exposure.
Access should be protected through strong authentication, appropriate permissions, and secure connectivity controls.
-
Inconsistent Endpoint Protection
Devices at branch locations may not always receive the same security policies as head-office systems.
Centralised endpoint management helps maintain consistent protection across locations.
-
Limited Visibility
If security teams cannot see what is happening at remote sites, suspicious activity may go undetected for longer.
Centralised logging and monitoring can provide greater visibility across distributed environments.

Agentic AI for Operations Leaders: Turning AI into Action
Optimising Site Networks for Security
Network security should begin with understanding how traffic moves through each location.
Organisations should consider:
- Which users access which systems
- Which applications require internet connectivity
- Which devices need access to internal resources
- How sites communicate with headquarters
- How cloud applications are accessed
- Where sensitive information flows
This allows security teams to design controls around actual business requirements rather than relying on generic configurations.
Segmentation Can Limit the Impact of an Attack
Network segmentation is particularly valuable for businesses operating multiple sites.
Instead of allowing every device to communicate freely, organisations can separate environments such as:
- Corporate devices
- Guest Wi-Fi
- IoT devices
- Printers
- Operational systems
- Servers
If one device is compromised, segmentation can help prevent attackers from moving easily across the environment.
Protecting Cloud-Connected Sites
Modern sites are increasingly dependent on cloud services.
Employees may access Microsoft 365, Azure-hosted applications, CRM systems, ERP platforms, and other SaaS services directly from branch locations.
This means site security can no longer focus only on the physical network perimeter.
Identity, device compliance, cloud access, and application security need to work together.
Microsoft Entra ID, Conditional Access, endpoint security, and cloud security controls can help organisations establish consistent security regardless of where users connect from.
Site Security Monitoring
Security optimisation should not stop after implementation.
Ongoing monitoring helps organisations identify:
- Suspicious network activity
- Unusual login behaviour
- Endpoint threats
- Configuration changes
- Failed authentication attempts
- Potential policy violations
Centralised monitoring provides security teams with a broader view of the environment and can reduce the time required to identify and respond to incidents.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
A Practical Site Security Optimisation Approach
1. Assess
Review network infrastructure, devices, access controls, connectivity, and security configurations across each location.
2. Identify
Prioritise vulnerabilities and configuration weaknesses according to business impact and risk.
3. Standardise
Create consistent security policies and configurations across sites wherever practical.
4. Secure
Implement appropriate controls across firewalls, endpoints, identities, wireless networks, and cloud access.
5. Monitor
Establish continuous visibility into security events and unusual activity.
6. Review
Regularly reassess site security as the business, technology environment, and threat landscape change.
Why Choose Exigo Tech
At Exigo Tech, we help organisations strengthen security across distributed environments while keeping technology practical and manageable.
Our capabilities include:
- Site security assessments
- Network security optimisation
- Firewall configuration reviews
- Wireless security
- Endpoint security
- Microsoft Entra ID and Conditional Access
- Cloud security
- Network segmentation
- Security monitoring
- Managed IT and cybersecurity services
Our approach helps organisations create a consistent security baseline across locations while identifying site-specific risks that require additional attention.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

