MDR vs SOC Services: Understanding the Difference for Modern Businesses
 Niten Devalia
Chief Sales Officer / Co-founder • Sep 21, 2026 • 6 min read
Cybersecurity has moved beyond simply installing antivirus software and firewalls. Modern businesses need continuous visibility into threats, rapid response capabilities, and security expertise that can keep pace with an increasingly complex technology environment.
Two terms frequently appear in conversations about modern cybersecurity: Managed Detection and Response (MDR) and Security Operations Centre (SOC) services.
Although they are closely related, they are not the same thing.
Understanding the difference is important when deciding how your organisation should detect, investigate, and respond to cyber threats. The right approach depends on your internal capabilities, security maturity, technology environment, and business requirements.
At Exigo Tech, we help organisations navigate these options as their Managed Intelligence Partner, combining security technology, specialist expertise, and ongoing monitoring to strengthen cyber resilience.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
What Is a Security Operations Centre (SOC)?
A Security Operations Centre is a dedicated function responsible for monitoring and managing an organisation’s cybersecurity environment.
A SOC typically brings together people, processes, and technologies to provide continuous visibility across security systems.
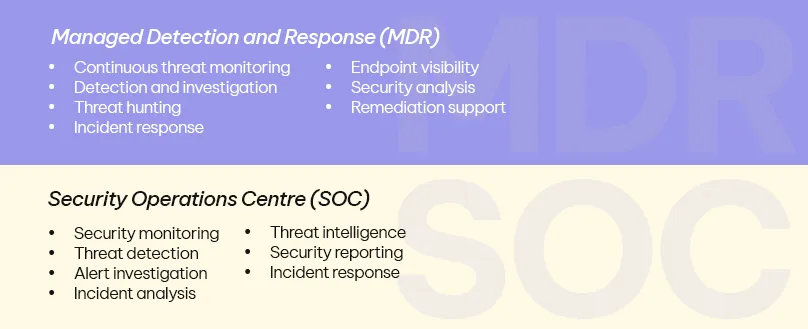
Its responsibilities can include:
- Security monitoring
- Threat detection
- Alert investigation
- Incident analysis
- Threat intelligence
- Security reporting
- Incident response
A SOC may be operated internally by an organisation or provided through an external security services provider.
The important point is that a SOC represents the security operations capability, rather than one specific security product.
What Is Managed Detection and Response (MDR)?
Managed Detection and Response is a cybersecurity service focused specifically on identifying and responding to threats.
An MDR service typically combines security technologies with security analysts who investigate suspicious activity and take action when threats are identified.
MDR commonly provides:
- Continuous threat monitoring
- Detection and investigation
- Threat hunting
- Incident response
- Endpoint visibility
- Security analysis
- Remediation support
The service is generally designed to provide organisations with specialist detection and response capabilities without requiring them to build and operate an entire security team internally.
MDR vs SOC: What’s the Difference?
The terms are sometimes used interchangeably, but there is an important distinction.
A SOC is the operational security function, while MDR is a managed security service focused on detection and response.
Think of a SOC as the broader security operations capability. MDR can be one of the services delivered by that capability.
A SOC may perform a wide range of activities, while MDR is generally centred on identifying threats, investigating them, and responding to incidents.

Agentic AI for Operations Leaders: Turning AI into Action
How a Traditional SOC Works
An organisation operating its own SOC typically needs to establish several components.
People
Security analysts, engineers, incident responders, and security specialists are required to monitor and investigate threats.
Technology
The SOC may use platforms such as:
- Security Information and Event Management (SIEM)
- Endpoint Detection and Response (EDR)
- Extended Detection and Response (XDR)
- Threat intelligence platforms
- Security orchestration tools
Processes
The team needs defined processes for:
- Alert triage
- Incident escalation
- Investigation
- Containment
- Recovery
- Reporting
Building all three components requires significant investment and ongoing management.
How MDR Works
MDR provides an alternative for organisations that don’t want to build all of these capabilities internally.
The MDR provider typically manages the detection and response function on behalf of the customer.
Depending on the service, this can include monitoring endpoints, identities, cloud environments, and other security signals.
When suspicious activity is detected, security analysts investigate the event and help determine whether action is required.
This provides businesses with access to specialist security capabilities without having to maintain an entire internal detection and response operation.
Key Differences Between MDR and SOC Services
| Area | SOC Services | MDR Services |
| Primary purpose | Broader security operations | Detection and response |
| Monitoring | Continuous, depending on service | Continuous monitoring is typically central |
| Threat investigation | Yes | Yes |
| Incident response | Yes | Core capability |
| Threat hunting | Often available | Commonly included |
| Security expertise | Requires or provides dedicated analysts | Provided as part of managed service |
| Infrastructure | May require significant investment | Provider-managed |
| Internal resources | Can require substantial staffing | Lower internal operational requirement |
| Scope | Can cover broader security operations | Focused primarily on threat detection and response |
The exact services vary between providers, so organisations should assess the scope of each offering rather than relying solely on the terminology.
Which Approach Fits an SMB?
For small and medium-sized businesses, building a full internal SOC can be challenging.
Organisations may struggle to recruit enough security specialists to provide continuous coverage while also managing the cost of security platforms and infrastructure.
MDR can provide a practical way to access specialist detection and response capabilities without establishing a complete internal SOC.
This can be particularly useful for businesses that already have internal IT teams but lack dedicated cybersecurity resources.
When a SOC May Be Appropriate
A dedicated SOC may be appropriate for organisations with:
- Large security teams
- Complex technology environments
- Extensive compliance requirements
- High volumes of security events
- Dedicated security budgets
- Requirements for greater operational control
Some larger organisations also use a hybrid model, combining internal security operations with external managed services.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Why MDR Is More Than Security Monitoring
One of the biggest misconceptions about managed security is that it simply means watching alerts.
Effective MDR goes further.
Security analysts investigate suspicious activity to determine whether it represents a genuine threat. Depending on the service, they may also support containment, remediation, threat hunting, and incident response.
This human element is important because security platforms can generate large volumes of alerts. Organisations need expertise to distinguish genuine threats from routine activity.
How MDR Fits Into a Broader Security Strategy
MDR should not operate in isolation.
It works alongside other security controls, including:
- Identity protection
- Endpoint security
- Email security
- Cloud security
- Vulnerability management
- Security awareness
- Data protection
- Backup and recovery
For organisations using Microsoft technologies, platforms such as Microsoft Defender and Microsoft Sentinel can form important components of a broader security ecosystem.
The objective is to create connected security capabilities rather than relying on a single tool or service.
Why Choose Exigo Tech as Your Managed Intelligence Partner
At Exigo Tech, we help organisations build security operations capabilities aligned with their business requirements and technology environment.
As your Managed Intelligence Partner, our Managed Security as a Service offering can bring together:
- Managed Detection and Response
- 24/7 security monitoring
- Microsoft Defender
- Microsoft Sentinel
- Threat detection and investigation
- Incident response
- Endpoint and identity security
- Security posture management
- Ongoing security advisory
We work across technology, security, and business priorities to help organisations move from reactive security management towards continuous protection and optimisation.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

