How to Prepare for Ransomware Attacks: A Practical Guide for Australian Businesses
 Niten Devalia
Chief Sales Officer / Co-founder • Jul 24, 2026 • 5 min read
Ransomware continues to be one of the most disruptive cyber threats facing businesses today.
What was once an opportunistic attack targeting individual computers has evolved into a highly organised criminal business model. Modern ransomware groups use sophisticated tactics to gain access, steal sensitive data, disable backups, and disrupt entire business operations before demanding payment.
For Australian organisations, the impact can be significant. Beyond financial losses, ransomware incidents can result in operational downtime, regulatory obligations, reputational damage, and loss of customer trust.
The good news is that ransomware preparedness is not just about preventing attacks; it is about building the ability to detect, respond, and recover quickly.
At Exigo Tech, we help organisations strengthen their cyber resilience as their Managed Intelligence Partner, combining proactive security, continuous monitoring, and practical recovery strategies to reduce the impact of ransomware attacks.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
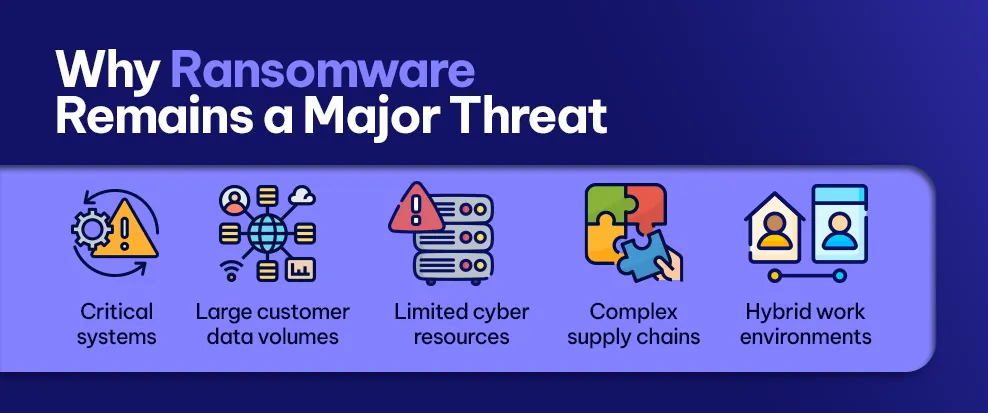
Why Ransomware Remains a Major Threat
Ransomware attacks have become more targeted and more sophisticated.
Rather than attacking random victims, cybercriminals now focus on organisations where operational disruption is likely to create pressure to pay a ransom.
Businesses of all sizes are targeted, particularly those with:
- Critical business systems
- Large amounts of customer data
- Limited cybersecurity resources
- Complex supply chains
- Hybrid work environments
Today’s ransomware attacks often involve both data encryption and data theft, increasing pressure on organisations to respond quickly.
How Ransomware Attacks Typically Begin
Most ransomware attacks do not start with malware.
They begin with access.
Common entry points include:
- Phishing emails
- Compromised credentials
- Weak passwords
- Unpatched systems
- Remote access vulnerabilities
- Third-party compromises
Once attackers gain access, they often spend time exploring the environment before launching the ransomware itself.
This makes early detection just as important as prevention.
Build Strong Identity Security
Identity protection is one of the most effective ways to reduce ransomware risk.
Organisations should implement:
- Multi-Factor Authentication (MFA)
- Microsoft Entra ID
- Conditional Access
- Role-Based Access Control (RBAC)
- Privileged Identity Management (PIM)
Strong identity controls make it significantly harder for attackers to establish a foothold within the environment.

Agentic AI for Operations Leaders: Turning AI into Action
Keep Systems Updated
Many ransomware groups exploit known vulnerabilities that already have security patches available.
A structured patch management process should include:
- Operating systems
- Applications
- Servers
- Network devices
- Third-party software
Regular updates reduce the number of opportunities attackers can exploit.
Strengthen Endpoint Protection
Every endpoint connected to the business network should be protected.
Modern endpoint security includes:
- Endpoint Detection and Response (EDR)
- Behaviour-based threat detection
- Anti-malware protection
- Device compliance monitoring
- Automated threat response
These capabilities improve the likelihood of detecting suspicious activity before ransomware is deployed.
Protect Your Microsoft 365 Environment
Microsoft 365 has become a primary business platform for many organisations.
Protecting this environment requires more than user authentication.
Businesses should review:
- User permissions
- Conditional Access policies
- Microsoft Defender configurations
- Email security
- SharePoint permissions
- OneDrive sharing settings
Strong Microsoft 365 governance reduces opportunities for attackers to move laterally after gaining access.
Maintain Reliable Backups
Backups remain one of the most important components of ransomware preparedness.
However, simply having backups is not enough.
Organisations should ensure backups are:
- Regularly tested
- Protected from unauthorised modification
- Stored separately from production systems
- Available for rapid recovery
Recovery planning should be treated as a business continuity exercise rather than solely an IT responsibility.
Develop an Incident Response Plan
Every organisation should know what to do before a ransomware incident occurs.
An incident response plan should define:
- Roles and responsibilities
- Escalation procedures
- Communication processes
- Technical response actions
- Recovery priorities
Practising response procedures helps reduce confusion during a real incident.
Monitor Continuously
Many ransomware attacks involve days or even weeks of preparation before encryption begins.
Continuous monitoring helps identify:
- Suspicious logins
- Privilege escalation
- Unusual file activity
- Data exfiltration
- Malware behaviour
Security Operations Centres (SOC) and Managed Detection and Response (MDR) services improve visibility across the environment and support faster response times.
Educate Employees
Technology alone cannot eliminate ransomware risk.
Employees should understand how to recognise:
- Phishing emails
- Suspicious links
- Social engineering attempts
- Unusual authentication requests
- Unexpected file downloads
Regular security awareness training remains one of the most valuable investments organisations can make.
Adopt a Zero Trust Approach
Modern ransomware often spreads by exploiting excessive trust within corporate environments.
Zero Trust reduces this risk by continuously verifying users, devices, and applications before granting access.
Key Zero Trust principles include:
- Least-privilege access
- Identity verification
- Device compliance
- Network segmentation
- Continuous monitoring
These controls help limit the impact of compromised accounts and reduce opportunities for lateral movement.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Cyber Resilience Matters More Than Prevention Alone
No security strategy can guarantee complete protection against every cyber threat.
This is why organisations increasingly focus on cyber resilience.
Cyber resilience combines:
- Prevention
- Detection
- Response
- Recovery
Businesses that prepare across all four areas recover faster, minimise operational disruption, and strengthen long-term resilience.
Preparedness is no longer measured solely by how well organisations prevent attacks; it is measured by how effectively they continue operating when incidents occur.
Why Choose Exigo Tech as Your Managed Intelligence Partner
At Exigo Tech, we help organisations strengthen ransomware preparedness through practical cybersecurity strategies tailored to their business environment.
As your Managed Intelligence Partner, we provide:
- Zero Trust cybersecurity assessments
- Microsoft 365 Security Health Checks
- Managed Security as a Service (MSaaS)
- Security Operations Centre (SOC)
- Managed Detection and Response (MDR)
- Microsoft Defender implementation
- Backup and disaster recovery consulting
- Ongoing cybersecurity monitoring and advisory services
Our approach helps organisations reduce ransomware risk while improving operational resilience and long-term security maturity.
Preparation Is Your Best Defence Against Ransomware
Ransomware continues to evolve, but organisations that prepare proactively are far better positioned to withstand its impact.
Strong identity security, modern endpoint protection, reliable backups, continuous monitoring, and well-tested incident response plans work together to reduce both the likelihood and consequences of an attack.
Rather than waiting until a ransomware incident occurs, businesses should invest in building resilience today. A proactive cybersecurity strategy not only protects systems and data; it protects business continuity, customer trust, and the organisation’s ability to operate with confidence in an increasingly complex threat landscape.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

