Supply Chain Cybersecurity Risks: Protecting Your Business Beyond Your Own Network
 Niten Devalia
Chief Sales Officer / Co-founder • Jul 8, 2026 • 6 min read
Modern businesses rely on a growing ecosystem of vendors, cloud platforms, Software-as-a-Service (SaaS) applications, managed service providers, and third-party integrations.
From accounting software and CRM platforms to cloud storage, payment gateways, and collaboration tools, these external services enable organisations to operate more efficiently and innovate faster.
However, every new vendor or integration also introduces a potential cybersecurity risk.
Today’s attackers increasingly target supply chains because compromising one trusted partner can provide access to hundreds, or even thousands, of connected organisations.
For Australian businesses, managing supply chain cybersecurity is no longer optional. It has become a critical component of overall cyber resilience.
At Exigo Tech, we help organisations strengthen cybersecurity across their entire technology ecosystem as their Managed Intelligence Partner, ensuring vendors, SaaS platforms, and integrations are managed with security and governance in mind.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
What Is Supply Chain Cybersecurity?
Supply chain cybersecurity refers to protecting an organisation from risks introduced by third-party providers, software vendors, cloud services, contractors, and technology partners.
Rather than attacking an organisation directly, cybercriminals often compromise a trusted supplier and use that relationship to gain access to customer systems, sensitive information, or business operations.
Because these relationships are built on trust, supply chain attacks can be particularly difficult to detect.
Why Supply Chain Attacks Are Increasing
Businesses today use more third-party technology than ever before.
A typical organisation may rely on multiple external providers for:
- Cloud infrastructure
- Microsoft 365 applications
- Customer relationship management (CRM)
- Enterprise Resource Planning (ERP)
- Payroll and HR platforms
- Backup services
- Collaboration tools
- Payment systems
- API integrations
Each connection expands the organisation’s digital ecosystem and its potential attack surface.
Attackers recognise that compromising a single supplier can create opportunities to target multiple organisations simultaneously.
Common Supply Chain Cybersecurity Risks
-
Third-Party Software Vulnerabilities
Software vendors regularly release updates and new features.
If vulnerabilities exist within these applications, attackers may exploit them before organisations have an opportunity to apply security updates.
Regular patch management and vendor monitoring help reduce this risk.
-
SaaS Platform Security
Cloud applications simplify business operations but also introduce new security considerations.
Common risks include:
-
- Weak user access controls
- Misconfigured permissions
- Inadequate multi-factor authentication
- Excessive data sharing
- Poor identity management
Proper governance across SaaS environments is essential for protecting business information.
-
API and System Integrations
Many business applications exchange information through APIs and automated integrations.
If these connections are poorly secured, attackers may gain unauthorised access to systems or sensitive data.
Regular reviews of integrations help ensure they remain secure and necessary.
-
Vendor Access
Suppliers often require access to business systems to provide support or services.
Without appropriate controls, vendor accounts can become attractive targets for cybercriminals.
Organisations should regularly review:
-
- Vendor permissions
- Administrative access
- Remote connections
- Authentication requirements
Applying the principle of least privilege helps minimise unnecessary exposure.

Agentic AI for Operations Leaders: Turning AI into Action
Why SaaS Governance Matters
Many organisations now operate primarily through cloud-based applications.
While SaaS platforms reduce infrastructure complexity, they also create governance challenges.
Without central oversight, organisations may experience:
- Unapproved software adoption
- Duplicate applications
- Data stored across multiple platforms
- Inconsistent security policies
- Limited visibility into user activity
Strong SaaS governance improves both security and operational efficiency.
The Business Impact of Supply Chain Attacks
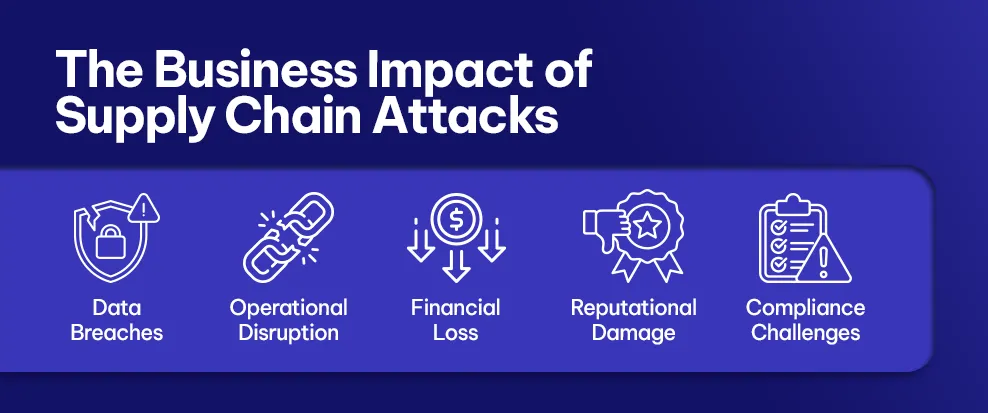
A compromise affecting one supplier can quickly become a business-wide incident.
Potential consequences include:
-
Data Breaches
Sensitive customer, financial, or operational information may be exposed through compromised third-party systems.
-
Operational Disruption
Critical business applications may become unavailable, interrupting normal operations.
-
Financial Loss
Incident response, recovery, regulatory obligations, and business disruption can create significant costs.
-
Reputational Damage
Customers expect organisations to protect their information, even when third parties are involved.
A supply chain incident can damage trust and affect long-term relationships.
-
Compliance Challenges
Organisations remain responsible for protecting information even when it is processed by external providers.
Effective vendor governance supports ongoing compliance obligations.
Building a Strong Supply Chain Security Strategy
Supply chain cybersecurity should extend beyond traditional IT security controls.
Assess Vendor Security
Before engaging a new supplier, organisations should evaluate:
- Security certifications
- Compliance standards
- Identity management
- Incident response capabilities
- Data protection practices
Security should be part of the procurement process rather than an afterthought.
Apply Least-Privilege Access
Third-party providers should only receive the access necessary to perform their responsibilities.
Regular reviews help ensure permissions remain appropriate over time.
Strengthen Identity Management
Identity remains one of the most effective security controls.
Implement:
- Multi-factor authentication
- Conditional Access
- Strong password policies
- Privileged Identity Management (PIM)
These controls reduce the likelihood of compromised vendor accounts being exploited.
Monitor Third-Party Activity
Continuous monitoring provides greater visibility into:
- Unusual login activity
- Data access patterns
- Administrative changes
- Integration behaviour
Early detection allows organisations to respond before incidents escalate.
Review SaaS Applications Regularly
Many businesses accumulate cloud applications over time.
Regular assessments help identify:
- Unused applications
- Duplicate services
- Unapproved software
- Security configuration issues
This reduces unnecessary complexity while improving governance.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Supply Chain Security and Zero Trust
Many organisations are adopting Zero Trust principles to strengthen supply chain security.
Rather than automatically trusting users or systems based on their location or relationship, Zero Trust verifies every access request.
This approach includes:
- Continuous identity verification
- Device compliance checks
- Least-privilege access
- Continuous monitoring
- Risk-based access decisions
Zero Trust helps reduce the impact of compromised vendors, users, or integrations.
Why Supply Chain Cybersecurity Is a Business Issue
Supply chain security extends beyond IT departments.
Procurement, legal, compliance, finance, operations, and executive leadership all influence how third-party risk is managed.
A coordinated approach helps organisations:
- Improve governance
- Reduce operational risk
- Strengthen resilience
- Meet regulatory expectations
- Support secure digital transformation
Cybersecurity should be embedded throughout the supplier lifecycle—from selection through ongoing management.
Why Choose Exigo Tech as Your Managed Intelligence Partner
At Exigo Tech, we help organisations secure their entire technology ecosystem, not just their internal infrastructure.
As your Managed Intelligence Partner, we provide:
- Third-party security assessments
- Cloud and SaaS security reviews
- Microsoft 365 security optimisation
- Identity and access management
- Zero Trust cybersecurity assessments
- Managed Security as a Service (MSaaS)
- Vendor risk and governance consulting
- Ongoing cybersecurity monitoring and support
Our approach helps organisations manage supply chain risk while supporting business growth and digital transformation.
Strong Cybersecurity Extends Beyond Your Organisation
Today’s businesses are more connected than ever before.
Every vendor, SaaS platform, cloud service, and integration contributes to operational success but also expands the potential attack surface.
Managing supply chain cybersecurity requires visibility, governance, and continuous assessment across your entire technology ecosystem.
By treating third-party security as a strategic priority, organisations can reduce risk, improve resilience, and build stronger trust with customers, partners, and stakeholders.
Table of Contents
Tags
Related Articles

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments
MDR vs SOC Services: Understanding the Difference for Modern Businesses

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

