- Technologies
- Dynamics 365 Business Central Workshop
- Dynamics 365 Supply Chain Management Workshop
- Dynamics 365 Finance Readiness Assessment
- Dynamics 365
- Customer Data Platform
- Dynamics 365 Sales
- Dynamics 365 Service
- Dynamics 365 Marketing
- Dynamics 365 Supply Chain Management
- Dynamics 365 Business Central
- Dynamics 365 Finance
- Dynamics 365 Project Management
- Modern Application Development
- Dynamics 365 for Sales Workshop
- Innovation
- Contact us
Identity-Based Attacks: How Microsoft Entra ID Helps Defend Against MFA Bypass and Token Theft
 Niten Devalia
Chief Sales Officer / Co-founder • Jul 17, 2026 • 6 min read
For many years, cybersecurity focused on protecting networks, servers, and endpoints.
Today, the primary target has shifted.
Cybercriminals are increasingly attacking identities rather than infrastructure, because compromising a trusted user account often provides everything they need to move through an organisation.
Whether through sophisticated phishing campaigns, session token theft, MFA bypass techniques, or identity misconfigurations, attackers are finding new ways to access business systems without exploiting traditional vulnerabilities.
As organisations continue adopting AI, Microsoft 365, cloud services, and hybrid work models, identity security has become one of the most important pillars of modern cybersecurity.
At Exigo Tech, we help organisations strengthen identity protection as their Managed Intelligence Partner, combining Microsoft security technologies with proactive governance and continuous monitoring to reduce identity-related risks.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
Why Identity Has Become the New Security Perimeter
Modern businesses no longer operate within a clearly defined corporate network.
Employees access business applications from:
- Home offices
- Mobile devices
- Cloud applications
- Customer sites
- Remote locations
Applications themselves are increasingly cloud-based, with Microsoft 365, Azure, Dynamics 365, and SaaS platforms becoming central to business operations.
In this environment, identity, not the network, determines who can access business resources.
As a result, attackers now focus on compromising user identities rather than attempting to breach traditional network defences.
Common Identity-Based Attacks
Identity attacks continue to evolve as security controls improve.
Several attack methods have become particularly common in modern Microsoft environments.
-
Credential Phishing
Credential phishing remains one of the most effective attack techniques.
Modern phishing campaigns use AI-generated content, legitimate-looking login pages, and highly personalised messaging to persuade users to reveal their credentials.
Once attackers obtain usernames and passwords, they attempt to access cloud services before security teams can respond.
-
MFA Bypass Attacks
Multi-Factor Authentication (MFA) remains one of the strongest security controls available, but attackers increasingly look for ways to bypass it.
Common techniques include:
- MFA fatigue attacks
- Adversary-in-the-Middle (AiTM) phishing
- Social engineering
- Session hijacking
Rather than attacking MFA directly, cybercriminals often manipulate users into unknowingly approving authentication requests or capturing authenticated sessions.
Strong MFA should therefore be combined with additional identity protection controls.
-
Session Token Theft
When users successfully authenticate, applications issue session tokens that allow continued access without requiring repeated logins.
If attackers steal these tokens, they may gain access to Microsoft 365 services without needing the user’s password or triggering another MFA challenge.
Token theft has become increasingly common because it enables attackers to bypass traditional authentication mechanisms.
Protecting authenticated sessions is now just as important as protecting passwords.
-
OAuth and Consent-Based Attacks
Many Microsoft 365 environments rely on third-party applications connected through OAuth.
Attackers increasingly exploit this trust by convincing users to grant malicious applications access to business data.
Instead of stealing credentials, they obtain legitimate permissions to:
- Read emails
- Access files
- View calendars
- Monitor communications
Strong application governance helps reduce this risk.
Why Microsoft Entra ID Plays a Critical Role
Microsoft Entra ID has become the foundation of identity management across Microsoft cloud environments.
It enables organisations to centrally manage:
- User identities
- Authentication
- Single Sign-On (SSO)
- Conditional Access
- Identity governance
- Privileged access
When properly configured, Entra ID provides multiple layers of protection that significantly reduce the risk of identity compromise.
However, these capabilities require ongoing configuration, monitoring, and optimisation.
Building a Strong Identity Security Strategy
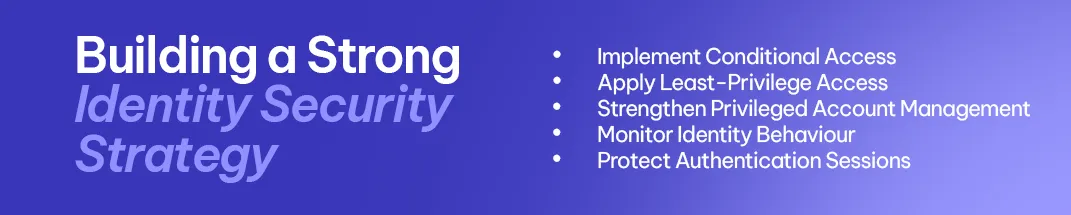
Identity protection should extend beyond passwords and MFA.
-
Implement Conditional Access
Conditional Access evaluates multiple factors before granting access, including:
-
- User identity
- Device compliance
- Location
- Sign-in risk
- Application being accessed
This creates more intelligent access decisions based on risk rather than simple authentication.
-
Apply Least-Privilege Access
Users should only receive the permissions required to perform their roles.
Regular reviews help identify:
- Excessive permissions
- Dormant accounts
- Administrative access
- Legacy accounts
Reducing unnecessary privileges limits the impact of compromised identities.
-
Strengthen Privileged Account Management
Administrative accounts remain attractive targets for attackers.
Microsoft Entra Privileged Identity Management (PIM) enables organisations to:
-
- Reduce standing administrative privileges
- Approve elevated access
- Audit privileged activity
- Implement time-based access
This significantly strengthens identity security.

Agentic AI for Operations Leaders: Turning AI into Action
-
Monitor Identity Behaviour
Continuous monitoring helps identify:
-
- Impossible travel activity
- Suspicious sign-ins
- Unusual authentication patterns
- Excessive permission requests
- High-risk users
Early detection often prevents attackers from establishing persistence.
-
Protect Authentication Sessions
Organisations should complement MFA with controls that reduce token-related risks.
These include:
-
- Session management policies
- Risk-based authentication
- Continuous access evaluation
- Secure browser and device policies
Protecting authenticated sessions is increasingly important as attackers evolve.
Identity Security and Zero Trust
Identity protection sits at the heart of every Zero Trust strategy.
Rather than automatically trusting authenticated users, Zero Trust continuously evaluates access requests throughout each session.
This includes:
- Identity verification
- Device compliance
- Behaviour analysis
- Risk assessment
- Least-privilege enforcement
Together, these controls help reduce the effectiveness of identity-based attacks.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Preparing for the Future
Identity attacks will continue evolving alongside advances in AI and automation.
Businesses should focus on:
- Strengthening identity governance
- Improving visibility
- Modernising authentication
- Reviewing application permissions
- Educating users
- Continuously monitoring identity activity
Security strategies must evolve as quickly as attacker techniques.
Organisations that treat identity as a strategic security capability will be better prepared for future threats.
Why Choose Exigo Tech as Your Managed Intelligence Partner
At Exigo Tech, we help organisations strengthen identity security across Microsoft environments through practical, business-focused cybersecurity strategies.
As your Managed Intelligence Partner, we provide:
- Microsoft Entra ID implementation and optimisation
- Identity and access management consulting
- Conditional Access configuration
- Microsoft Defender deployment
- Zero Trust cybersecurity assessments
- Managed Security as a Service (MSaaS)
- Security Operations Centre (SOC)
- Ongoing identity governance and monitoring
Our goal is to help organisations protect their most valuable security asset, their identities.
Identity Security Is Business Security
As cloud adoption continues to grow, identity has become the primary target for modern cybercriminals.
Protecting user accounts now requires more than strong passwords or basic MFA.
A modern identity security strategy combines Microsoft Entra ID, Conditional Access, least-privilege principles, continuous monitoring, and Zero Trust architecture to reduce risk and improve resilience.
By investing in identity protection today, organisations can better defend against evolving threats while enabling secure access to the applications and data that drive their business.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

