- Technologies
- Dynamics 365 Business Central Workshop
- Dynamics 365 Supply Chain Management Workshop
- Dynamics 365 Finance Readiness Assessment
- Dynamics 365
- Customer Data Platform
- Dynamics 365 Sales
- Dynamics 365 Service
- Dynamics 365 Marketing
- Dynamics 365 Supply Chain Management
- Dynamics 365 Business Central
- Dynamics 365 Finance
- Dynamics 365 Project Management
- Modern Application Development
- Dynamics 365 for Sales Workshop
- Innovation
- Contact us
User Application Hardening: Reducing the Everyday Tools Attackers Exploit
 Niten Devalia
Chief Sales Officer / Co-founder • Mar 4, 2026 • 5 min read
Most cyberattacks do not begin with highly sophisticated hacking techniques. They begin with everyday applications.
Web browsers. PDF readers. Microsoft Office. Email clients. Media players.
These are tools employees use daily. They are trusted, widely installed, and often overlooked from a security perspective. But they are also among the most targeted applications by attackers.
This is why User Application Hardening is a critical control within the Essential Eight. It focuses on reducing the attack surface within commonly used applications by disabling unnecessary features and strengthening default configurations.
At Exigo Tech, we see User Application Hardening as a practical and highly effective way to reduce risk without disrupting business operations.
What Is User Application Hardening?
User Application Hardening involves configuring commonly used applications in a way that limits their ability to be exploited.
Instead of allowing all features to run by default, organisations:
- Disable unnecessary functionality.
- Restrict high-risk features.
- Block untrusted content.
- Enforce secure configuration policies.
The objective is simple: reduce the ways attackers can use legitimate software to execute malicious activity.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
Why Everyday Applications Are a Prime Target
Attackers prefer using legitimate applications because:
- They are already installed.
- They are trusted by users.
- They are often allowed through firewalls.
- Security tools may not flag them as suspicious.
Instead of bringing in obvious malware, attackers use built-in features within legitimate tools to execute commands, download payloads, or move laterally.
If applications are not hardened, attackers can exploit:
- Browser scripting engines.
- Embedded Office content.
- PDF active content.
- Unrestricted add-ins or extensions.
- Automatic file execution behaviours.
Hardening reduces these opportunities significantly.
Why User Application Hardening Is Essential Eight–Critical
The Essential Eight prioritises controls that block common exploitation techniques.
Many real-world breaches involve attackers leveraging:
- Malicious browser scripts.
- Embedded Office content.
- Exploited PDF readers.
- Misused built-in features.
User Application Hardening directly addresses these risks by restricting how these applications behave. Rather than waiting to detect misuse, hardening prevents the misuse from being possible in the first place.
What Happens Without Application Hardening
When user applications are left in default configurations:
- Browsers may execute unsafe scripts.
- Office applications may process risky content
- PDF readers may allow active elements.
- Unnecessary features may expand the attack surface.
Over time, this creates multiple pathways for exploitation. Even well-managed organisations can be compromised if applications are left fully open and unrestricted.

Agentic AI for Operations Leaders: Turning AI into Action
What Does Good Application Hardening Look Like?
Effective hardening includes:
- Disabling unnecessary browser features.
- Blocking Flash and other outdated plugins.
- Restricting ActiveX controls.
- Disabling unnecessary Office features.
- Preventing automatic execution of embedded content.
- Enforcing secure browser configurations.
- Managing and limiting extensions or add-ins.
The focus is not on removing functionality users need. It is on eliminating features that provide little business value but high security risk.
Benefits of User Application Hardening
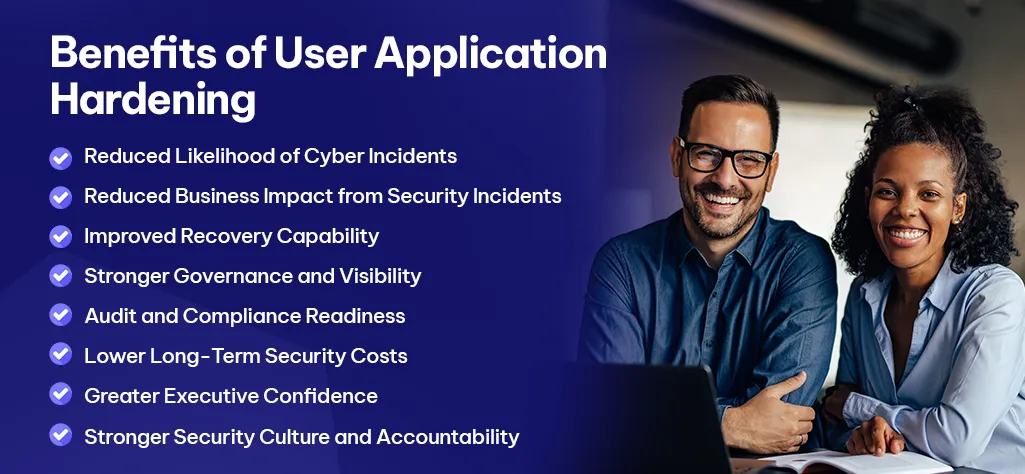
When implemented correctly, User Application Hardening delivers meaningful security and operational benefits.
- Reduced Likelihood of Cyber Incidents: By limiting exploitable features, attackers have fewer entry points.
- Reduced Business Impact from Security Incidents: Even if an attack attempt occurs, hardened applications reduce the ability to execute malicious code.
- Improved Recovery Capability: With fewer exploitation paths, containment and recovery become more manageable.
- Stronger Governance and Visibility: Application configurations are standardised and controlled across the environment.
- Audit and Compliance Readiness: Secure configuration management supports regulatory and security framework requirements.
- Lower Long-Term Security Costs: Preventing exploitation reduces the cost of incident response and downtime.
- Greater Executive Confidence: Leadership gains assurance that common attack vectors are being actively controlled.
- Stronger Security Culture and Accountability: Standardised configuration policies reinforce consistent security practices across teams.
Common Mistakes Organisations Make
User Application Hardening is often misunderstood or inconsistently applied.
Common mistakes include:
- Relying on default settings.
- Hardening some applications but not others.
- Applying policies inconsistently across departments.
- Failing to review configurations after updates.
- Allowing unnecessary browser extensions.
- Treating hardening as a one-time task.
Security configurations must be maintained continuously.
Why Hardening Must Be Balanced with Usability
Some organisations hesitate to harden applications because they fear productivity disruption.
However:
- Most risky features are rarely needed for daily work.
- Hardening can be tested and phased.
- Exceptions can be controlled and documented.
- Policies can be refined over time.
When implemented intelligently, users often do not notice the changes, but attackers certainly do.

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
How User Application Hardening Supports Other Controls
User Application Hardening works alongside:
- Application Control.
- Restricting Administrative Privileges.
- Multi-Factor Authentication.
- Patch Management.
- Macro Restrictions.
Together, these controls create a layered defence.
If one control fails, another blocks the attack.
Security strength comes from combining preventative measures.
Why Choose Exigo Tech to Implement User Application Hardening
User Application Hardening requires:
- Configuration expertise.
- Environment-wide visibility.
- Policy consistency.
- Ongoing monitoring.
As your Managed Intelligence Partner, we:
- Review current application configurations.
- Identify high-risk features.
- Design hardened policy baselines.
- Implement structured rollouts.
- Monitor compliance and effectiveness.
- Continuously refine configurations as threats evolve.
We ensure that everyday applications become controlled tools, not silent vulnerabilities.
Small Adjustments, Significant Risk Reduction
User Application Hardening may seem like a subtle control. But its impact is powerful.
By limiting unnecessary functionality within common applications, organisations significantly reduce the opportunity for exploitation.
It is a practical, preventative, and high-value component of the Essential Eight framework.
Security does not always require dramatic change. Sometimes, it requires tightening the small gaps that attackers rely on.
Table of Contents
Tags
Related Articles
Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

