- Technologies
- Dynamics 365 Business Central Workshop
- Dynamics 365 Supply Chain Management Workshop
- Dynamics 365 Finance Readiness Assessment
- Dynamics 365
- Customer Data Platform
- Dynamics 365 Sales
- Dynamics 365 Service
- Dynamics 365 Marketing
- Dynamics 365 Supply Chain Management
- Dynamics 365 Business Central
- Dynamics 365 Finance
- Dynamics 365 Project Management
- Modern Application Development
- Dynamics 365 for Sales Workshop
- Innovation
- Contact us
Compliance and Cybersecurity Challenges Facing Australia’s Finance Industry
 Niten Devalia
Chief Sales Officer / Co-founder • Aug 28, 2026 • 5 min read
Australia’s finance industry operates in an environment where trust, availability, and data protection are inseparable from business performance.
Banks, lenders, insurers, superannuation funds, payment providers, fintechs, and other financial organisations manage highly sensitive information while relying on interconnected digital platforms, cloud services, third-party providers, and real-time transactions.
That makes the sector an attractive target for cybercriminals.
For financial organisations, cybersecurity is not simply about preventing attacks. It is about protecting customers, maintaining critical services, managing third-party risk, and demonstrating operational resilience.
At Exigo Tech, we help Australian financial organisations strengthen cybersecurity, compliance, and resilience as their Managed Intelligence Partner.

How to Secure Microsoft Copilot Agents with Microsoft 365 E5
Why Financial Organisations Are High-Value Targets
Financial organisations hold information and assets that are valuable to attackers.
This includes:
- Customer identity information
- Financial records
- Payment information
- Account information
- Transaction data
- Investment information
- Authentication credentials
- Business and regulatory records
Cybercriminals can target this information for financial fraud, extortion, identity theft, or resale.
The sector also operates systems where downtime can have immediate consequences.
A disruption to payment processing, customer portals, banking platforms, or internal systems can affect customers and business operations simultaneously.
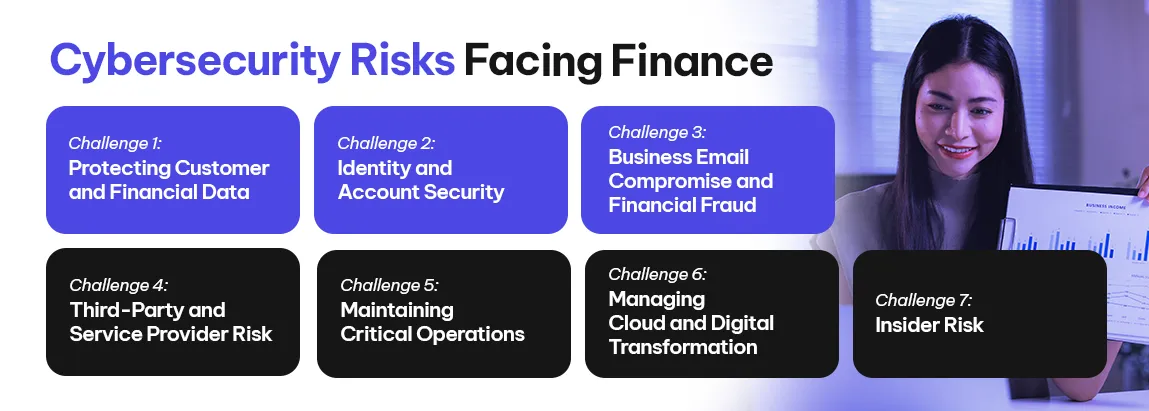
Challenge 1: Protecting Customer and Financial Data
Financial organisations must protect significant volumes of sensitive information.
Strong data protection requires more than perimeter security.
Organisations need to control:
- Who can access information
- What information they can access
- Where information is stored
- How it is shared
- How long it is retained
- How it is protected throughout its lifecycle
Data classification, encryption, access controls, monitoring, and governance all contribute to reducing the risk of unauthorised access.

Agentic AI for Operations Leaders: Turning AI into Action
Challenge 2: Identity and Account Security
Identity is one of the most important security boundaries in modern financial environments.
Employees, customers, contractors, applications, and administrators may all require access to digital services.
Attackers increasingly target identities through:
- Phishing
- Credential theft
- MFA attacks
- Token theft
- Session hijacking
- Social engineering
Financial organisations need strong identity controls that go beyond simply enabling MFA.
Microsoft Entra ID, Conditional Access, Privileged Identity Management, risk-based authentication, and least-privilege access can help create stronger identity security.
Challenge 3: Business Email Compromise and Financial Fraud
Financial organisations are particularly exposed to attacks that combine technical compromise with social engineering.
Attackers may compromise an employee account and monitor communications before attempting to manipulate a payment, redirect funds, or impersonate a trusted party.
Security therefore needs to extend beyond email filtering.
Finance and procurement teams should also have strong verification and approval processes for sensitive transactions.
Challenge 4: Third-Party and Service Provider Risk
Modern financial organisations depend on technology partners, cloud providers, SaaS platforms, payment services, and other external providers.
This creates additional risk.
Third-party risk management should therefore include:
- Vendor security assessments
- Access reviews
- Contractual security requirements
- Service-level expectations
- Incident notification requirements
- Ongoing monitoring
A supplier should not become an unmanaged pathway into a financial organisation’s environment.
Challenge 5: Maintaining Critical Operations
Cybersecurity and operational resilience are closely connected in finance.
An organisation may have strong preventive controls and still experience an incident.
The more important question becomes:
Can critical services continue while the organisation responds and recovers?
This makes resilience planning a central part of financial-sector risk management.
Organisations should regularly test:
- Backup recovery
- Disaster recovery
- Incident response
- Business continuity
- Communication procedures
- Critical supplier dependencies

Microsoft 365 Security for Healthcare Providers: Protecting Patient Data and Business Operations
Challenge 6: Managing Cloud and Digital Transformation
Financial organisations increasingly use cloud infrastructure and SaaS applications to improve scalability and agility.
However, cloud adoption introduces new security considerations.
Common risks include:
- Excessive permissions
- Misconfigured services
- Weak identity controls
- Inadequate logging
- Unmanaged SaaS applications
- Poorly governed data
Cloud security should therefore be incorporated into the organisation’s broader risk and compliance framework.
Challenge 7: Insider Risk
Not every security incident originates outside the organisation.
Employees and contractors may accidentally expose information or deliberately misuse access.
Financial organisations should use least-privilege access, access reviews, monitoring, DLP, and appropriate offboarding processes to reduce this risk.
Building a Finance Cybersecurity and Compliance Strategy
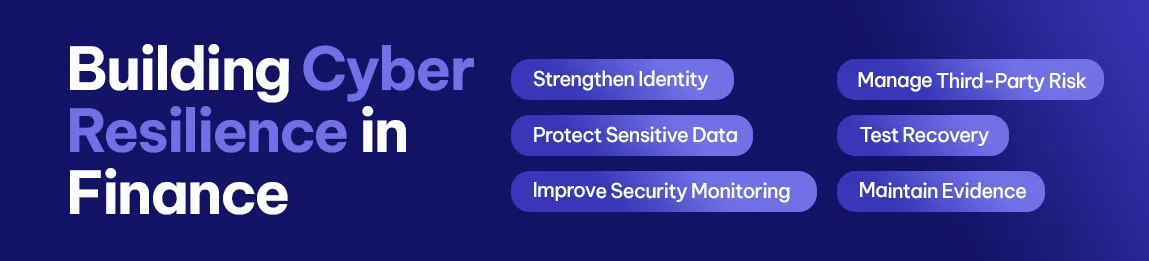
A mature strategy should bring security, compliance, and operational resilience together.
-
Strengthen Identity
Use strong authentication, Conditional Access, privileged access controls, and regular identity reviews.
-
Protect Sensitive Data
Apply classification, encryption, DLP, and access controls across customer and financial information.
-
Improve Security Monitoring
Continuous monitoring helps detect suspicious activity before it develops into a major incident.
-
Manage Third-Party Risk
Assess suppliers before onboarding them and continue reviewing their security and operational resilience.
-
Test Recovery
Regularly test backups, disaster recovery, and incident response procedures rather than assuming they will work when needed.
-
Maintain Evidence
Compliance requires more than having controls in place. Organisations should be able to demonstrate how those controls are managed, monitored, and reviewed.
Why Choose Exigo Tech
At Exigo Tech, we help Australian financial organisations strengthen technology environments while aligning cybersecurity with business and regulatory requirements.
Our capabilities include:
- Financial Services Cybersecurity Assessments
- Microsoft 365 Security Health Checks
- Microsoft Entra ID and identity security
- Managed Security as a Service (MSaaS)
- Security monitoring and incident response
- Cloud security and governance
- Data protection and Microsoft Purview
- Essential Eight assessments
- Zero Trust cybersecurity assessments
- Third-party and operational risk advisory
Our approach combines technology, security expertise, governance, and ongoing management to help organisations build stronger resilience.
Table of Contents
Tags
Related Articles

Endpoint Security for SMBs: Protecting Devices, Users and Business Data
Compliance and Cybersecurity Challenges Facing Australian Local Governments
MDR vs SOC Services: Understanding the Difference for Modern Businesses

Let's Talk About Your IT Challenges
Book a free consultation with our experts today. We'll analyze your current infrastructure and provide actionable recommendations.

